Hackers attack refrigerators: from supermarkets to blood banks
USD 21,65
Popular
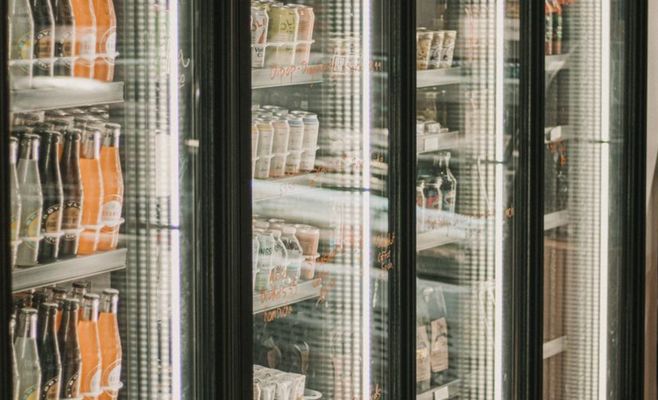
US agencies, including the FBI and the cybersecurity agency CISA, have warned of a growing threat: hackers are breaking into industrial refrigeration systems and turning fridges into ovens. In October and early November, hundreds of supermarkets in France were hit, along with stores in Belgium and Sweden, and in France the attack even reached stores of donated plasma.
Alarms saved the blood
The scale of the problem is illustrated by a case described by Brett Leatherman, head of the FBI's cyber division. In early November, attackers got into the cooling systems at three sites of the French national blood transfusion service EFS, where blood plasma was stored. The alarm went off, staff reacted in time, and not a single unit of blood was lost, Leatherman confirmed.
The episode clearly shows that the consequences of such attacks go far beyond empty shelves in a shop. The warning was prepared not only by the FBI and CISA but also by the US departments of health, agriculture and transportation. The same technologies protect food in retail, medicines, medical supplies and cargo in transit.
How hackers heat up freezers
The criminals target the electronic units that control the temperature and operation of refrigeration equipment. Vulnerabilities include missing updates, unprotected access from the internet and incorrect settings. Once inside a system, hackers can change the temperature or switch on a permanent defrost and heating mode.
The warning describes several methods of intrusion, including bypassing the login and injecting their own code. There is also a risk that staff simply stop seeing the real temperature. Besides spoiled stock, this threatens equipment failure, fire and danger to people if they eat improperly stored food.
Leatherman also pointed to a mundane cause: some devices still run on factory-default passwords that can be found in the manufacturer's manual. Remote control helps not only the service technician but also the uninvited guest.
A new wave in Europe
European bodies have confirmed that the October incidents are not behind us. The EU cybersecurity agency ENISA, in a statement dated November 4, reported a new wave of cases on November 1 and 2 and urged organizations to secure vulnerable systems immediately.
Earlier this week, problems were reported at about forty Delhaize stores in Belgium and fifteen Carrefour stores. The Swedish chains ICA and Coop also reported outages. According to the Financial Times, temperatures in some Swedish freezers rose to 55 degrees Celsius.
In France, the October attack affected hundreds of supermarkets. According to Reuters, hackers changed the cooling settings and temperatures reached 50 degrees. Food that was supposed to stay fresh or frozen ended up in the bin.
The new US warning names neither the culprits nor their motives, and does not confirm that the same group is behind all of the cases.
What system owners are advised to do
“Disconnect these control units from the public internet,” Leatherman urged operators. If remote access is necessary, it should be shielded by a firewall.
The joint document also recommends separating production equipment from the regular corporate network, changing factory passwords and installing security updates. Outdated equipment that the manufacturer no longer supports should be gradually replaced. Safe temperature limits with alerts when they are exceeded are also important: the story of the French blood service showed how much depends on whether the alarm reaches the right people.
Around Prague, based on reporting by novinky.cz